


Most email security is built around the premise - is this message safe to let into the organization's perimeter?” But today’s account takeover attacks are creating harder problems. For instance, what happens when the attacker is not sending from a suspicious domain, spoofing an executive, or attaching obvious malware? Or what happens when the attacker is already inside a legitimate email account?
Most cyberattacks don’t look malicious anymore; rather, they’re as normal as they can be. An email arrives from a known vendor, the tone matches past conversations, the timing aligns with an active transaction... Nothing triggers suspicion until money moves or data leaks.
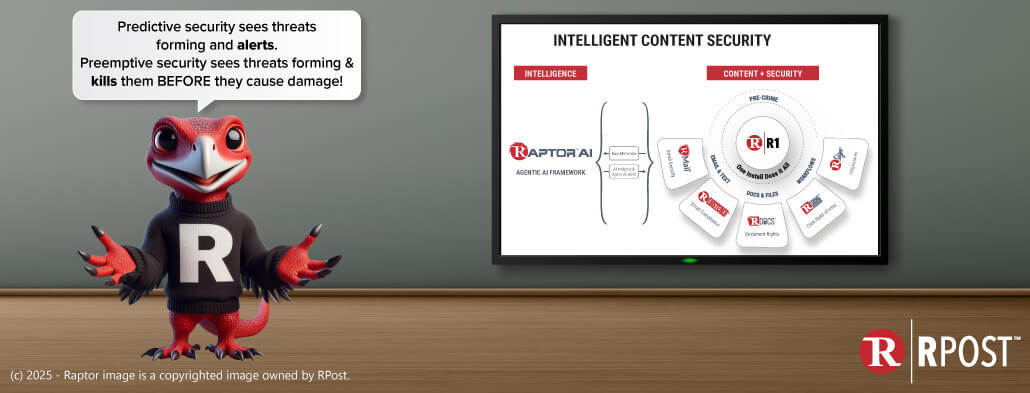
Rocky the raptor here, RPost’s pre-emptive cybersecurity product evangelist. Keith Fitz-Gerald, a well followed investment guru, wrote recently, “Cybersecurity isn’t sexy… Until you need it. By then, it’s too late.” This is often the challenge with risk mitigation products; cybersecurity is sort of like insurance --- but much more critical.

Armand here, RPost’s armadillo product evangelist. I was struck by a notification from a company that faced a data breach due to cybercriminal activity. In their breach notice, the breached company wrote, “…has taken steps to ensure that the stolen data will not be publicly shared or used maliciously.
Armand here again reporting for Tech Essentials. This week, I’m writing to you from…my mom’s basement. This is so that I can try and get in the mindset of a cybercriminal trying to leverage AI to perpetrate a sophisticated email scam.
September 25, 2026
August 21, 2026
July 31, 2026
July 06, 2026
June 19, 2026


